The internet is so cooked
What is happening right now?
So, I woke up on the 21st, and went about my day, but then I saw a bunch of vulnerabilities happening at once.
This is honestly one of the most wild weeks/months EVER LIKE WHAT THE FUCK
The most notable security vulnerability though, is: PHP2Shell.
(Also thanks https://bsky.app/profile/nightshade.technology for documenting most of this :3)
PHP2Shell
(Explanation of one of the exploits):
Apparently, you can exploit PHP when it runs out of memory (OOM error), it utilizes a low-level C function, and sometimes it may leave memory in an half-broken state, which leads to a remote code execution (RCE)
This is.. VERY BAD right now, because ~70% of the internet still runs on PHP.
The notable websites that went down were:
- DeviantArt
- WiKirby
- Alpine Linux Wiki
- FOSS Wiki
- Miraheze
- Wiki.gg
- 4chan
Sources:
- https://r74n.com/php
- https://bsky.app/profile/nightshade.technology/post/3mydptd5yjk2f
- https://bsky.app/profile/hailey.at/post/3myfj3tu3vs2q (lmfao)
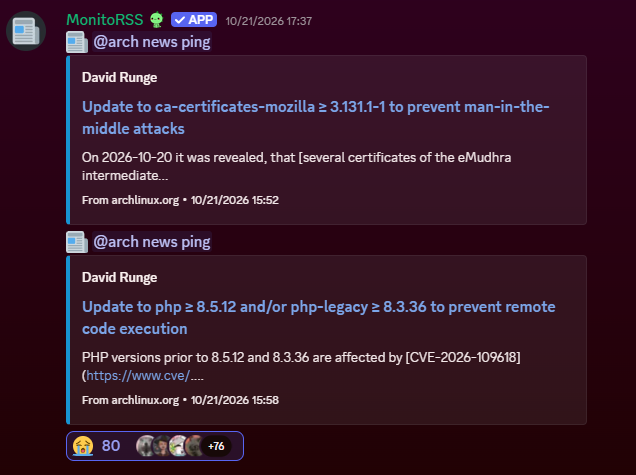
I’m pretty sure PHP is now mostly patched (but not really) but most of the web was offline, some sites still are, since there are other severe vulnerabilities to deal with too, yay!
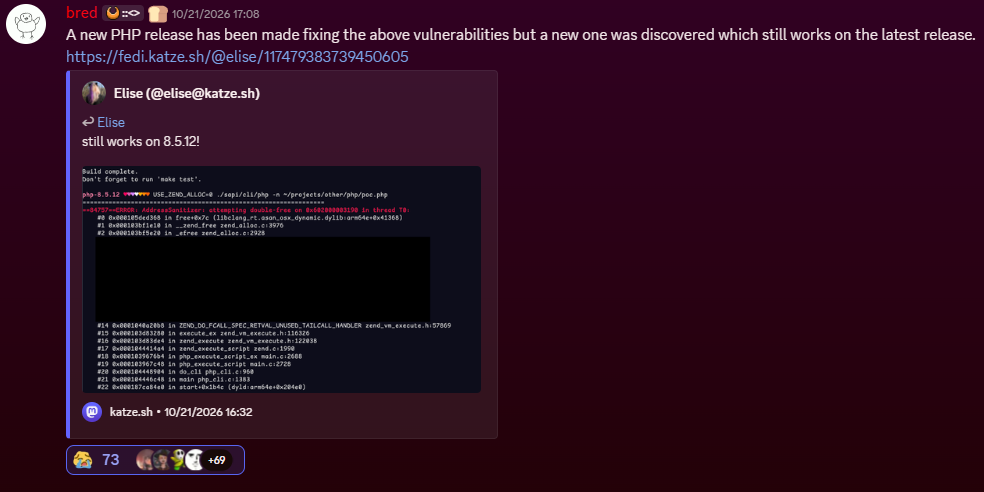
(The patched PHP versions are 8.5.12, 8.4.27, 8.3.36, 8.2.35)
Just, shutdown your servers in PHP for now and update your PHP please!!!! (until you update, keep it offline, after you update, turn your server back on)
https://bsky.app/profile/nightshade.technology/post/3myfbtrmdas27
eMudhra certs leak/with extremely weak keys
So, there was also 8 certificates that got leaked/had guessable keys.
And one of the cert’s private key was “4”, YES, JUST FUCKING “4”, WHY!!!
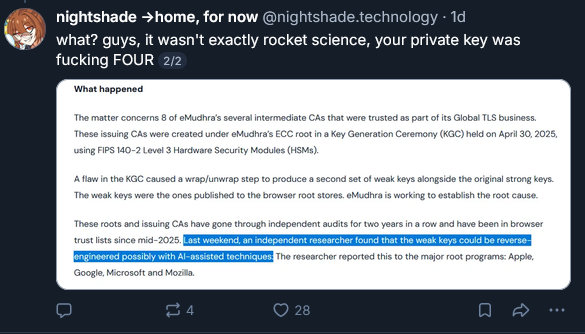
But the other certs also were leaked/had guessable keys cuz their keys were below 256, good shit good shit.
Check if your client still trusts them: https://emudhra.we-have-a-problem.com
After that, they also decided to leave the international TLS certificate business, lmfao
(pip needs 26.2.2 or newer and certifi 2026.10.19 or newer, since old pip keeps trusting the certificates regardless of the OS store. debian’s fixed package for trixie is 20250419+deb13u1)
Sources:
- https://bsky.app/profile/nightshade.technology/post/3myhrxkw44s2d
- https://emudhra.we-have-a-problem.com
- https://emudhra.com/en/press-release/emudhra-statement-distrust-global-tls-intermediate-root-ca
- https://arstechnica.com/security/2026/10/the-internet-goes-on-high-alert-after-discovery-of-8-compromised-tls-certs/
- https://bsky.app/profile/nightshade.technology/post/3myffljqujs2s
Check out https://bsky.app/profile/lampyt.lamps-dev.dev and scroll down to see some stuff I reposted about the NodeJS, PHP and eMudhra situations.
NodeJS and others
So, there are A BUNCH of other vulnerabilities!!!!
Gitlab (another FUCKING RCE WHAT THE FUCK): https://x.com/TheHackersNews/status/2112981939984671090
NodeJS: https://nodejs.org/en/blog/vulnerability/october-2026-security-releases, https://bsky.app/profile/nightshade.technology/post/3myil56elck2l
Ubuntu: https://bsky.app/profile/kastor.sh/post/3myfe2ap57k2l
Plex2Shell (sigh better update now!!!): https://thehackernews.com/2026/10/hackers-exploit-plex2shell-flaws-to.html
Apache traffic server (not httpd thank fuck): https://bsky.app/profile/nightshade.technology/post/3myg2rw7dmc2s
Railway (really): https://bsky.app/profile/nightshade.technology/post/3myg72rgevk2k
OpenCode: https://www.infosecurity-magazine.com/news/opencode-breach-openai-anthropic/
Apache Pulsar Manager (lmfao): https://bsky.app/profile/nightshade.technology/post/3myg7f5hwi22k
DNS in BIND (bruh): https://bsky.app/profile/nightshade.technology/post/3myg77emtbk2k
Linux Kernel Vulnerabilities leaked (lmfao): https://www.phoronix.com/news/LKML-New-Trend-Vulnerabilities
LiteLLM (docker and pypi got infected, lmfao): https://docs.litellm.ai/blog/security-incident-oct-21-2026
OVHcloud CLI (malware): https://thehackernews.com/2026/10/hackers-hijack-five-ovhcloud-cli.html
TeamUpdraft: https://teamupdraft.com/blog/security-incident-october-2026/
GhostAction (in the month, not week): https://cybersecuritynews.com/ghostaction-supply-chain-campaign/
Zeabur (its shutting down in december, RIP): https://cybernews.com/news/zeabur-cloud-provider-shutdown-two-breaches-3-million-records/
Tensorlake (in the month, not week): https://thehackernews.com/2026/10/tensorlake-npm-package-compromised-to.html
ConnectWise: https://thehackernews.com/2026/10/hackers-use-compromised-connectwise.html
Quest Diagnostics: https://cybersecuritynews.com/quest-diagnostics-hacked, https://x.com/AndrewCurran_/status/2113437710065311970
IDCF Cloud (in the month, not week): https://cybernews.com/security/japanese-cloud-cyberattack-railways-police-495-organizations-idcf/
VeloCloud: https://thehackernews.com/2026/10/arista-warns-of-critical-velocloud-sql.html
Atlassian (mostly patches): https://www.securityweek.com/atlassian-patches-75-third-party-flaws-in-data-center-and-server-products/
Pillow (python package, lmfao): https://thehackernews.com/2026/10/critical-flaw-in-pythons-popular-pillow.html
curl (HTTP/2 upload use-after-free, update to 8.23.0, mostly just crashes): https://thehackernews.com/2026/10/curl-patches-http2-upload-flaw-after.html
NGINX (5 flaws, all config dependent, update to 1.30.6 or 1.31.7): https://thehackernews.com/2026/10/nginx-fixes-5-flaws-including-possible.html
AnyDesk Linux (public pre-auth root exploit, update to 8.0.3+): https://thehackernews.com/2026/10/researchers-publish-working-exploit-for.html
Nextcloud + Collabora built-in CODE (web shells planted, update the app to 26.4.303+, disabling it isn’t enough): https://thehackernews.com/2026/10/hackers-backdoor-nextcloud-servers.html
PwnEscape (Linux kernel, guest VM can read host memory): https://thehackernews.com/2026/10/critical-pwnescape-linux-kernel.html
Vghost (Linux kernel vhost, local user to root, AI-assisted find lmfao): https://thehackernews.com/2026/10/ai-found-linux-kernel-flaw-gives-local.html
Next.js (two critical RCEs plus a DoS, update to 16.4.1 or 15.5.28): https://thehackernews.com/2026/10/nextjs-ships-out-of-band-patch-for-two.html
PAN-OS (authenticated RCE, already exploited a bit): https://thehackernews.com/2026/10/palo-alto-networks-patches-pan-os.html
Cisco Secure Email Gateway (unauthenticated file write to root, exploited): https://thehackernews.com/2026/10/cisco-warns-of-active-attacks.html
Sources:
- https://bsky.app/profile/nightshade.technology/post/3myfqvt6fl22f
- https://bsky.app/profile/kastor.sh/post/3myfe2ap57k2l
- https://bsky.app/profile/nightshade.technology/post/3myil56elck2l
This week/month is so fucking wild…
comments